Riley Günther · 28 October 2026
Transatlantic Data Rules Prompting Fresh Approaches to Workload Placement in Hybrid Setups
Transatlantic data rules continue to reshape how organizations manage workload placement in hybrid environments where on-premises systems connect with multiple cloud providers, and recent developments have accelerated those shifts. In October 2026 new compliance frameworks between the United States and European Union took effect following updates to adequacy decisions and cross-border transfer mechanisms that require stricter data residency controls and enhanced encryption standards for personal information moving between regions.
Regulatory Landscape Driving Placement Decisions
European regulators strengthened requirements under the General Data Protection Regulation while the United States expanded provisions within the Clarifying Lawful Overseas Use of Data Act, creating overlapping obligations that force technology teams to reassess where specific workloads run. Organizations now evaluate latency, cost, and performance against legal mandates that restrict certain data categories from leaving designated jurisdictions, and this evaluation process has led to increased adoption of localized processing nodes within hybrid architectures. Researchers at academic institutions across both continents have documented how these intersecting rules prompt companies to segment applications so sensitive datasets remain within approved geographic boundaries while less restricted workloads leverage global cloud resources.
Data sovereignty concerns intensified after the invalidation of prior transfer mechanisms, prompting reliance on standard contractual clauses supplemented by additional technical safeguards such as end-to-end encryption and access logging that satisfy supervisory authorities on both sides of the Atlantic. Industry reports indicate that hybrid setups allow finer control because teams can position database instances on-premises or in regional cloud zones while routing analytics workloads to centralized platforms that meet lower restriction thresholds.
Technical Adjustments in Hybrid Architectures
Cloud service providers responded by expanding availability zones in Europe and North America that align with updated certification programs, enabling customers to select placement options that satisfy transatlantic requirements without sacrificing operational efficiency. Workload orchestration tools now incorporate policy engines that factor in regulatory metadata alongside traditional metrics like CPU utilization and network bandwidth, and this integration helps automate decisions that previously required manual legal review. Teams deploy containerized applications with tagging systems that identify data sensitivity levels, allowing orchestration platforms to route traffic dynamically based on current rule interpretations.
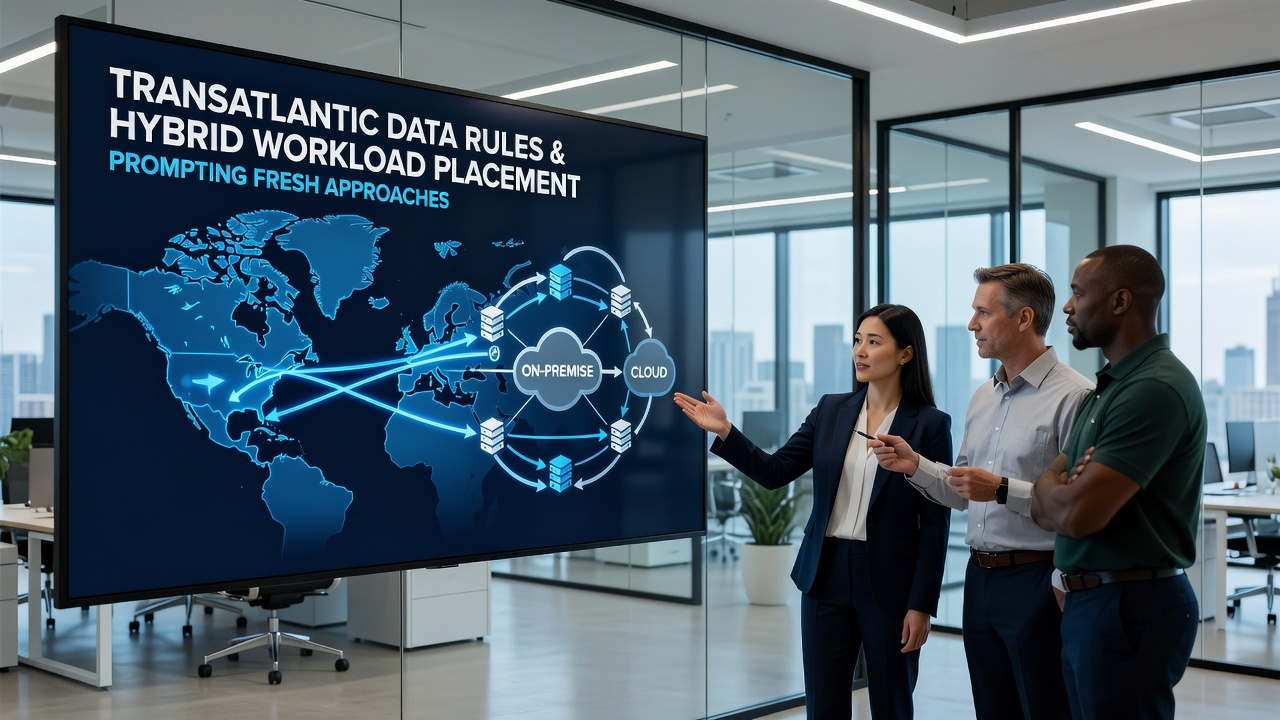
Encryption key management has emerged as another critical factor because some frameworks demand that keys remain under the control of entities subject to specific jurisdictions. Hybrid configurations accommodate this need through split-key architectures where master keys reside in on-premises hardware security modules while encrypted data moves across approved cloud regions. Observers note that these setups reduce exposure during audits because access logs demonstrate compliance with residency rules even when compute resources span multiple providers.
Case Examples from Industry Adoption
Financial services firms provide clear illustrations of these adaptations because they handle high volumes of personal and transaction data subject to both European and American oversight. One European bank reconfigured its hybrid environment to keep customer identification records on regional servers while shifting fraud detection models to a U.S.-based cloud instance that processes anonymized aggregates. Manufacturing companies followed similar patterns by anchoring supply chain data within domestic facilities yet distributing simulation workloads across certified transatlantic links that maintain audit trails required by regulators.
According to European Data Protection Board guidance, organizations must demonstrate that supplementary measures adequately protect data during transfer, and hybrid architectures offer the granular controls needed to meet that standard. U.S. Department of Commerce updates from the same period emphasized reciprocal obligations for American firms handling European data, reinforcing the need for documented placement policies that align with both frameworks.
Future Trajectory and Ongoing Adaptation
Technology vendors continue to release features that embed regulatory intelligence directly into infrastructure management consoles, reducing the manual effort required to maintain compliance across evolving rules. Academic studies project continued growth in demand for edge and regional processing capacity as organizations seek to minimize cross-border data movement while preserving the flexibility that hybrid models provide. Those patterns suggest workload placement strategies will remain fluid, adjusting whenever new adequacy findings or enforcement actions alter the legal baseline.
Conclusion
Transatlantic data regulations have established a persistent influence on hybrid cloud design, driving measurable changes in how teams select and manage workload locations. Organizations respond with segmented architectures, enhanced encryption practices, and policy-aware orchestration that balance performance requirements against legal constraints. Continued monitoring of regulatory updates remains essential for maintaining alignment as frameworks evolve on both sides of the Atlantic.